

Download Free Linux Foundation CKAD Exam Questions & Answer
Online VALID CKAD Exam Dumps File Instantly
The CKAD certification is highly valued in the industry and is recognized as a standard for Kubernetes application development skills. Linux Foundation Certified Kubernetes Application Developer Exam certification demonstrates that a developer has the skills and knowledge required to develop and deploy applications on Kubernetes clusters, and it can help developers stand out in a competitive job market. Linux Foundation Certified Kubernetes Application Developer Exam certification is also a valuable asset for organizations that are looking to hire Kubernetes developers, as it provides a measure of assurance that a candidate has the required skills and knowledge.
NEW QUESTION # 73
You have a Deployment named 'wordpress-deployment' that runs 3 replicas of a WordPress container. You need to implement a persistent volume claim (PVC) for each pod that stores the website data, and you want to ensure that the data persists even if the pod is deleted or restarted. The PVC should be created using a storage class named 'standard' with a capacity of 10Gi.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
I). Create a Storage Class:
- Create a 'standard' storage class: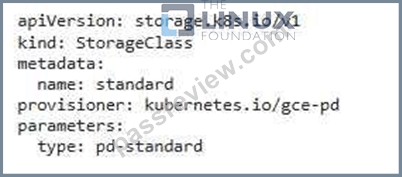
- Apply the YAML file: bash kubectl apply -f standard-storage-class-yaml 2. Create a Persistent Volume Claim: - Create a PVC named 'wordpress-pvc' with a request for IOGi storage and using the 'standard' storage class: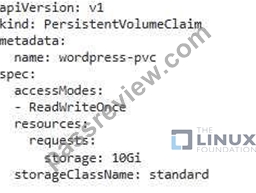
- Apply the YAML file: bash kubectl apply -f wordpress-pvc.yaml 3. Update the Deployment - Update the Swordpress-deployment' YAML file to mount the PVC to each pod: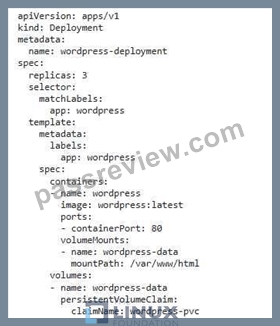
- Apply the updated YAML file: bash kubectl apply -f wordpress-deployment_yaml 4. Verify the Deployment - Check the status of the deployment using 'kubectl get deployments wordpress-deployment' to confirm the rollout and updated replica count. - Use 'kubectl describe pods -l app=wordpress' to confirm that each pod is using the 'wordpress-pvc' and the website data is stored in the persistent volume. - You can now access the WordPress website through the service that is associated with the Deployment. 5. Test Data Persistence: - Delete or restan one of the pods in the deployment. - Observe that the website data remains intact because the PVC is persistent and the data is stored in the underlying volume.,
NEW QUESTION # 74
You need to configure a Kubemetes Deployment to use a service account to access resources in a specific namespace. How can you create and assign a service account to your deployment, and how can you configure the service account to access resources in a different namespace?
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Service Account:
- Create a service account in the namespace where your deployment will run: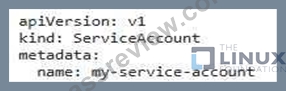
- Apply this YAML file using: bash kubectl apply -f service-account-yaml 2 Create a Role and Role8inding: - Define a role in the target namespace that the service account should have access to: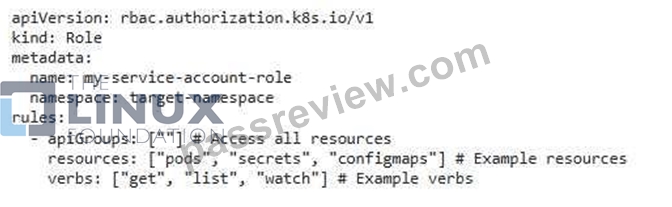
- Create a RoleBinding to bind the role to the service account: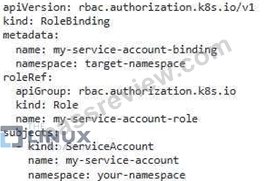
- Apply the Role and Role8inding YAML files using: bash kubectl apply -f role-yaml kubectl apply -f rolebinding.yaml 3. Modify your Deployment: - Update your Deployment YAML file to use the service account: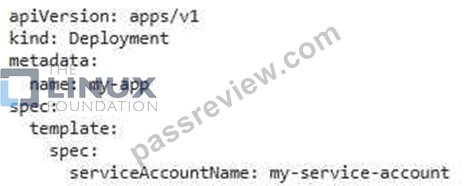
- Apply the updated deployment 4. Verify Access: - You can now use the service account to access resources in the target namespace. For example, you can create a pod that uses the service account and run a command to access resources.
NEW QUESTION # 75
You are developing a microservices application consisting of several deployments. One of the deployments, named 'order-service- deployments , is responsible for processing orders. Each order requires a specific backend service to process the order. You need to design a mechanism that automatically assigns an appropriate backend service to each order processing pod based on the order type. For example, orders for "books" should be assigned to the 'book-service' backend, while orders for "electronics" should be assigned to the 'electronics-service backend. Explain how you would implement this dynamic backend service assignment mechanism.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
This scenario requires a mecnanism to dynamically assign a backend service to each order processing pod based on the order type. Here's how you can implement this:
1. Label the Backend Services:
- Label the backend services based on the order type they handle. For instance:
- 'book-service': 'order.type=books'
- 'electronics-service: 'order.type=electronics'
2. I-Ise a ConfigMap:
- Create a ConfigMap named 'order-backend-mapping' that stores the mapping between order types and backend service labels.
- Use the ConfigMap to dynamically assign backend services based on the order type.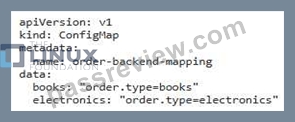
3. Modify the Order Service Deployment: - In the 'order-service-deployment , add an init container that retrieves the backend service mapping from the ConfigMap. - Use this mapping to determine the appropriate backend service for each order. - The init container can inject environment variables or modify the pod's annotations based on the mapping.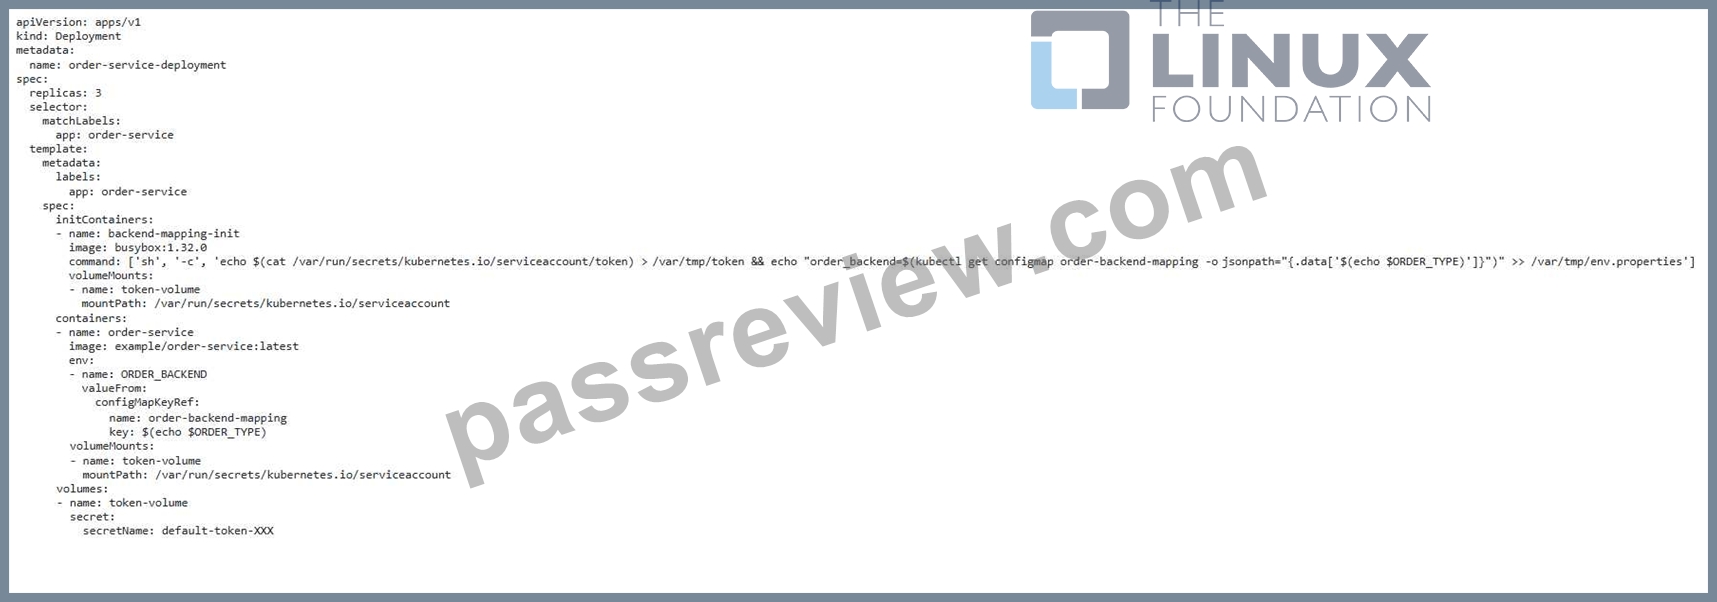
4. Update the Order Service: - Ensure the 'order-service' container is configured to use the environment variable set by the init container to access the correct backend service. 5. Deploy the Changes: - Apply the updated ConfigMap and Deployment using 'kubectl apply' 6. Test the Dynamic Assignment: - Create orders of different types and verity that the 'order-service' pods are automatically assigned the correct backend services. ,
NEW QUESTION # 76
You have a Deployment running a web application built With a Node.js container. The application currently uses an older version of the Node.js runtime, and you need to upgrade to a newer versiom Describe the steps involved in modifying the container image to include the new Node.js runtime without rebuilding the entire application.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Dockerfile:
- Create a new 'Dockerfile' With the following content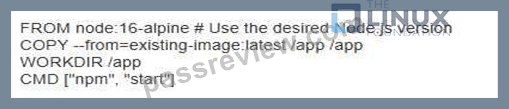
- Replace With the name of the existing Docker image used by your Deployment. - This Dockefflle uses a multi-stage build approach. It starts with a new Node.js base image and copies the application code from the existing image. This allows you to update the runtime without rebuilding the entire application. 2. Build the New Image: - Build tne image using the Dockerflle: docker build -t updated-image:latest 3. Update the Deployment - Modify your Deployment YAML file to use the newly built image: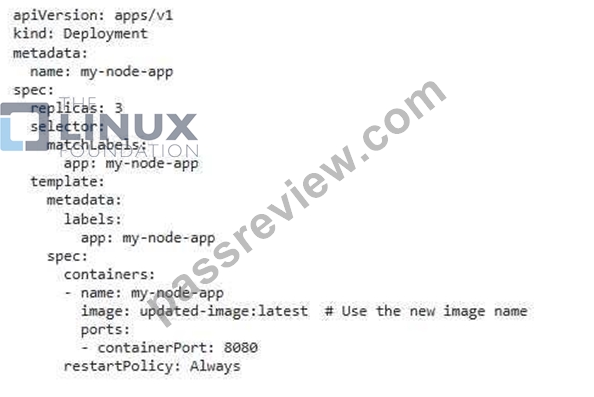
4. Apply the Changes: - Apply the updated Deployment using 'kubectl apply -f deployment.yamr. This will trigger a rolling update to the pods using the new image. 5. Verify the Update: - Check the logs of the pods using 'kubectl logs -f ' . You should see the application running with the updated Node.js version. 6. Test the Application: - Access your application and ensure it functions correctly with the new Node.js runtime.
NEW QUESTION # 77 
Task
Create a new deployment for running.nginx with the following parameters;
* Run the deployment in the kdpd00201 namespace. The namespace has already been created
* Name the deployment frontend and configure with 4 replicas
* Configure the pod with a container image of lfccncf/nginx:1.13.7
* Set an environment variable of NGINX__PORT=8080 and also expose that port for the container above
Answer:
Explanation:
See the solution below.
Explanation:
Solution: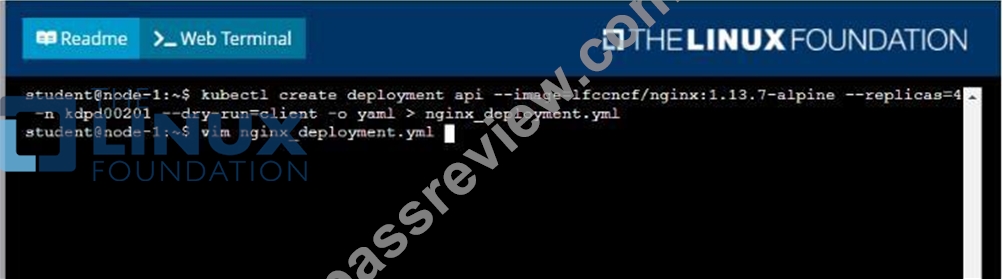
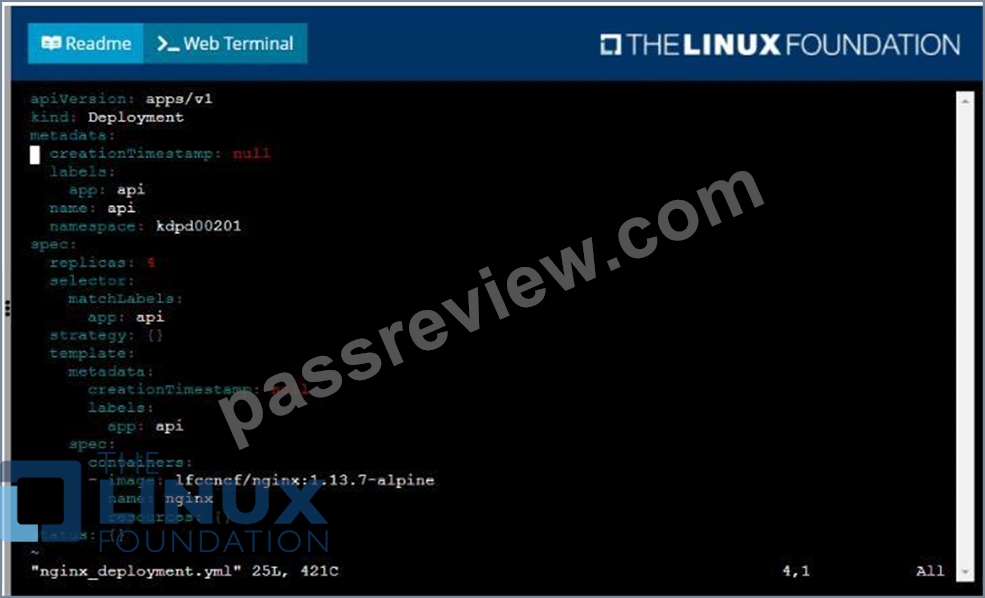
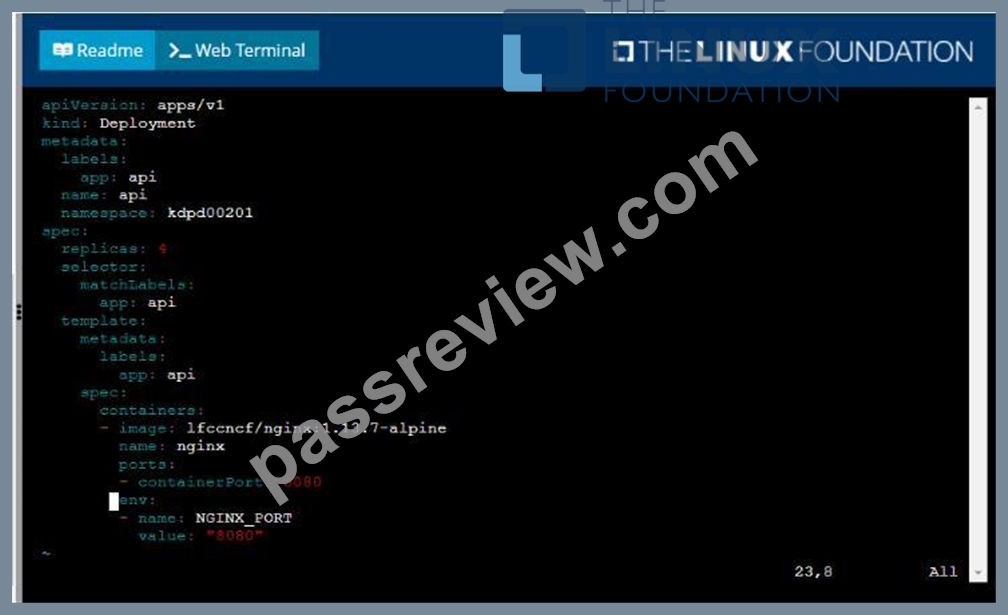
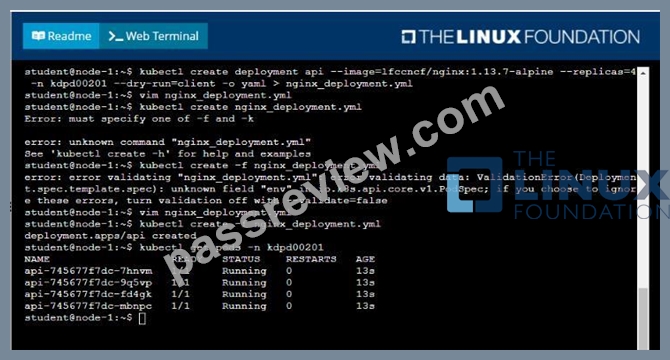
NEW QUESTION # 78
You have a Kubernetes cluster With a Deployment named 'my-app' running multiple replicas of your application. You need to ensure that only authorized users can access the application's pods through the Kubernetes APL Implement a role-based access control (RBAC) policy that allows only users in the "developers' group to access the pods of the 'my-app' Deployment.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Role: Define a Role that grants access to the 'my-app' Deployment pods.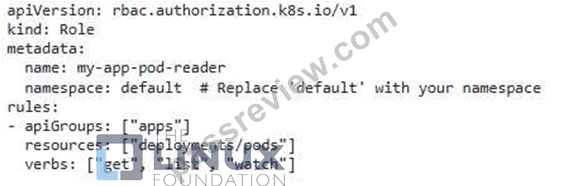
2. Create a RoleBinding: Bind the created Role to the 'developers' group.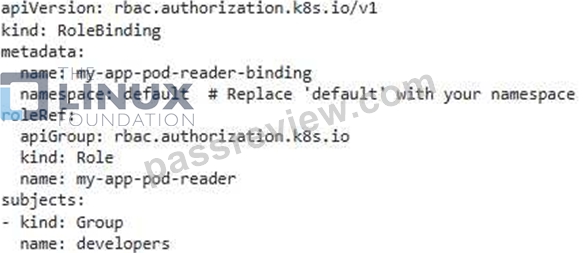
3. Apply the Role and RoleBinding: use 'kubectl apply' to create the Role and ROIeBinding resources. bash kubectl apply -f my-app-pod-readenyaml kubectl apply -f my-app-pod-reader-binding.yaml 4. Verify Access: Attempt to access the pods of the 'my-app' Deployment from a user in the "developers' group. You should be able to access the pods. Attempt to access the pods from a user not in the 'developers' group. You should receive an error indicating insufficient permissions.,
NEW QUESTION # 79
You are building a web application that requires environment-specific configurations, such as database connection details and API keys. You want to use ConfigMaps to manage these configurations in a secure and efficient way You have the following environment variables defined in your deployment YAML: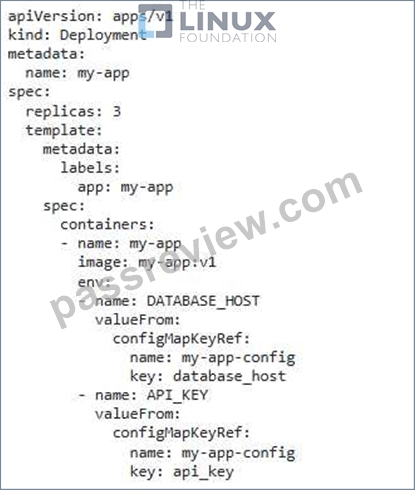
Create a ConfigMap named 'my-app-config' containing the following data: - 'database host: 'db.example.com' - 'api_key':
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create the ConfigMap: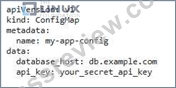
2. Apply the ConfigMap: bash kubectl apply -f my-app-config.yaml 3. Verify the ConfigMap: bash kubectl get configmap my-app-config -o yaml This command will display the created ConfigMap and its contents. 4. Deploy the Deployment: bash kubectl apply -f deploymentyaml The deployment Will now use the values from the ConfigMap to populate the environment variables within the containers. 5. Check the Pods: bash kubectl get pods -l app=my-app -o wide 6. Confirm Environment Variables: bash kubectl exec -it bash -c 'env' Replace with the name of one of the pods. This command will display the environment variables set within the container, including 'DATABASE HOST and 'API KEY'. Note: You should replace with your actual API key in the ConfigMap. This ensures that sensitive information is stored in a separate configuration file and not directly in the deployment YAML file.
NEW QUESTION # 80
You have a Deployment named 'redis-deployment that runs 3 replicas of a Redis container. You need to implement a rolling update strategy that allows tor a maximum ot one pod to be unavailable at any given time during tne update process, With the new pod becoming available before the old pod is terminated. Additionally, you want to ensure that the update process is triggered automatically whenever a new image is pushed to the Docker Hub repository 'redislabs/redis:latest.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Update the Deployment YAML:
- Update the 'replicas to 2_
- Define 'maxunavailable: 1 ' and 'maxSurge: 1 ' in the 'strategy.rollingupdate' section to control the rolling update process.
- Configure a 'strategy-type' to 'Rollingupdate' to trigger a rolling update when the deployment is updated.
- Add a 'spec-template.spec.imagePullPolicy: Always' to ensure that the new image is pulled even if it exists in the pod's local cache.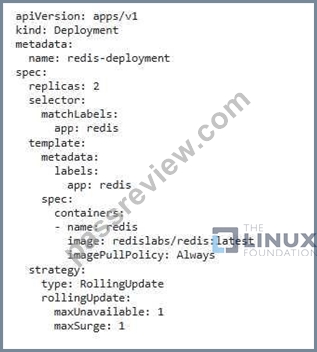
2. Create the Deployment: - Apply the updated YAML file using 'kubectl apply -f redis-deployment.yaml' 3. Verify the Deployment - Check the status of the deployment using 'kubectl get deployments redis-deployment' to confirm the rollout and updated replica count. 4. Trigger the Automatic Update. - Push a new image to the Docker Hub repository 5. Monitor the Deployment: - Use 'kubectl get pods -l app=rediS to monitor the pod updates during the rolling update process. You will observe that one new pod with the updated image is created, and then one old pod is terminated- This ensures that there is no downtime during the update process. 6. Check for Successful Update: - Once the deployment is complete, use 'kubectl describe deployment redis-deployment' to see that the 'updatedReplicaS field matches the 'replicas' field, indicating a successful update.
NEW QUESTION # 81
Exhibit:
Context
Your application's namespace requires a specific service account to be used.
Task
Update the app-a deployment in the production namespace to run as the restrictedservice service account. The service account has already been created.
- A. Solution:
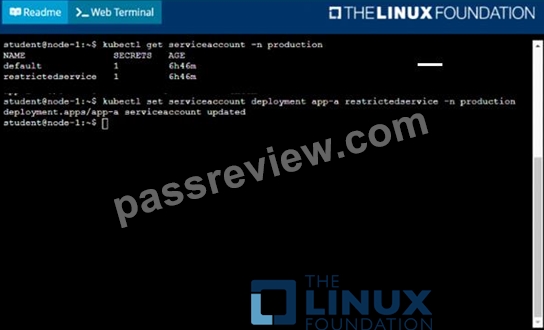
- B. Solution:
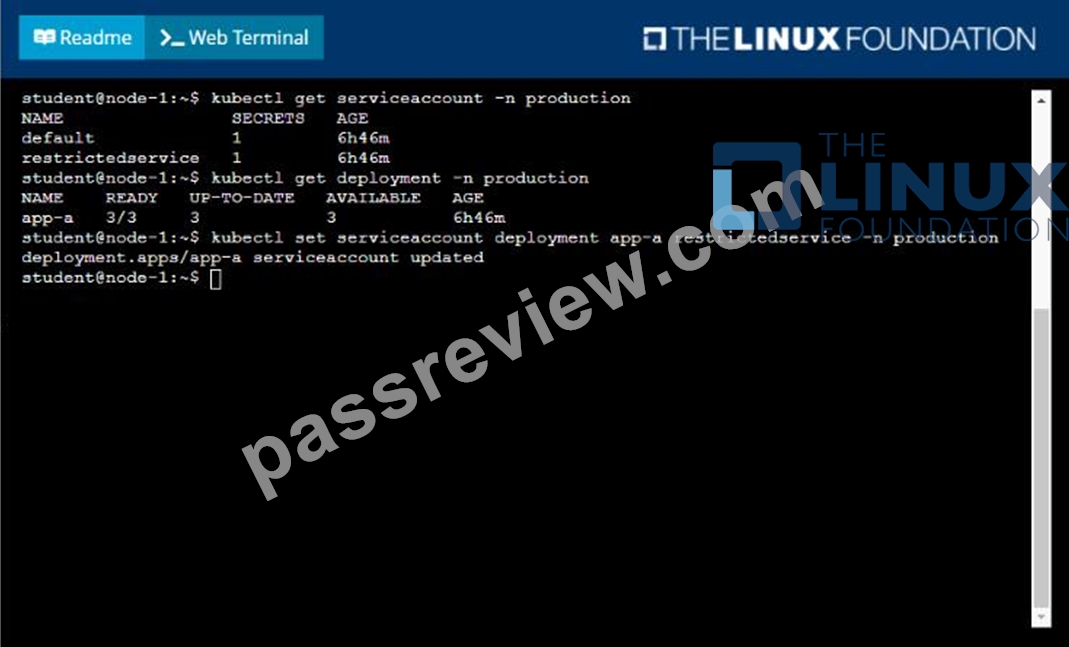
Answer: B
NEW QUESTION # 82
Exhibit:
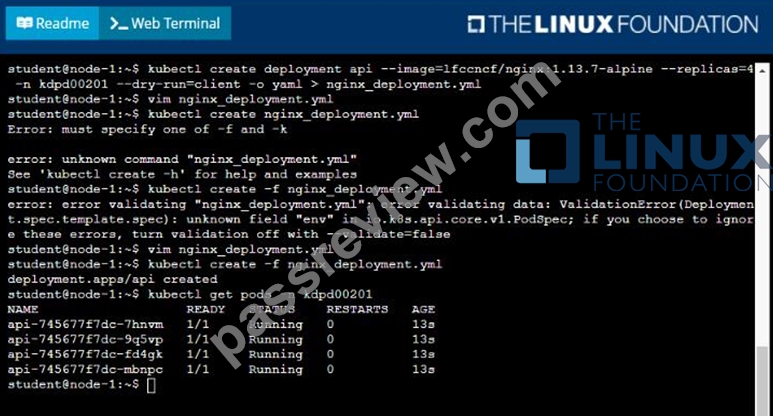
Task
Create a new deployment for running.nginx with the following parameters;
* Run the deployment in the kdpd00201 namespace. The namespace has already been created
* Name the deployment frontend and configure with 4 replicas
* Configure the pod with a container image of lfccncf/nginx:1.13.7
* Set an environment variable of NGINX__PORT=8080 and also expose that port for the container above
- A. Solution:
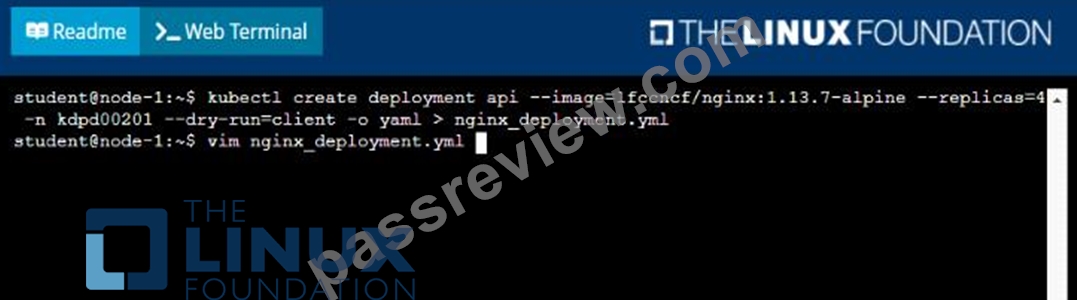
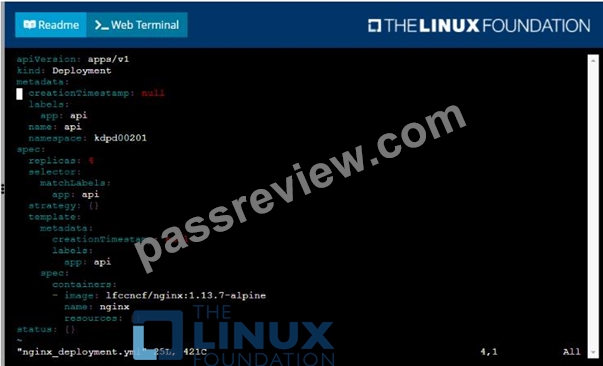
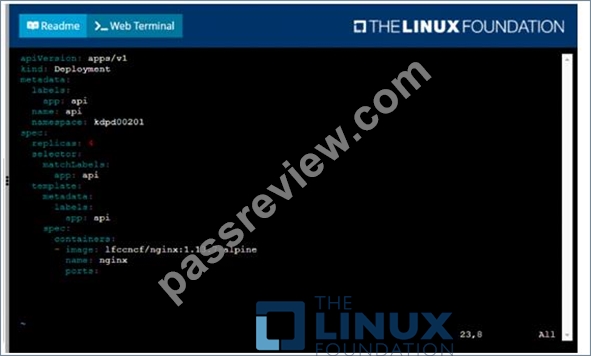
- B. Solution:
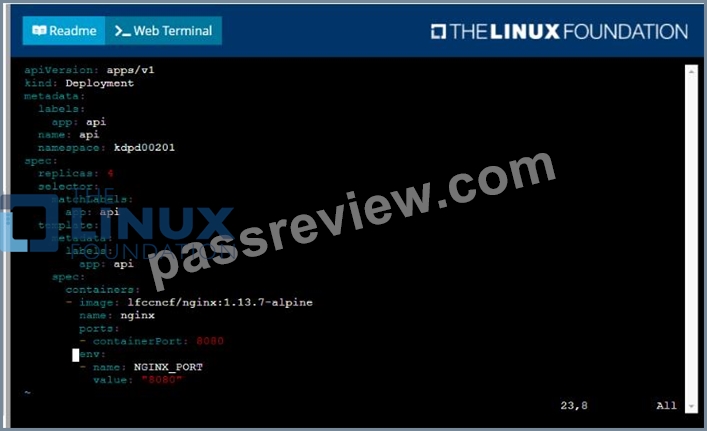
Answer: B
NEW QUESTION # 83
You have a Deployment named 'wordpress-deployment' that runs 3 replicas of a WordPress container. You want to implement a blue- green deployment strategy for this deployment This strategy should involve creating a new replica set with the updated image, and then gradually shitting traffic to the new replica set. After the traffic has been shifted, the old replica set should be deleted. This process should be fully automated whenever a new image is pushed to the Docker Hub repository 'example/wordpress:latest'
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Kubernetes Secret for Docker Hub Credentials:
- You'll need a Secret to securely store your Docker Hub credentials for pulling images. Create a Secret with the following YAML: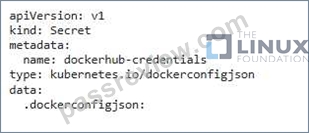
- Replace with the base64 encoded content of your Docker Hub credentials file. This file is typically named '~/.docker/config.json' and contains your Docker Hub username and password. You can create this file or update it manually. To encode the file, use a command like 'base64 ~/.docker/config .jsons 2. Create a ConfigMap for Deployment Configuratiom - Create a ConfigMap to hold the image name and any other deployment-specific configuration: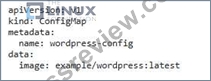
3. Define a Deployment with a Blue-Green Strategy: - Create a Deployment named swordpress-deployment that incorporates the blue-green deployment strategy. This Deployment will have a 'strategy' section with a 'type' of 'Recreate' (for initial deployment) and a 'blueGreenDeploymentStrategy' section: 4. Create a Service.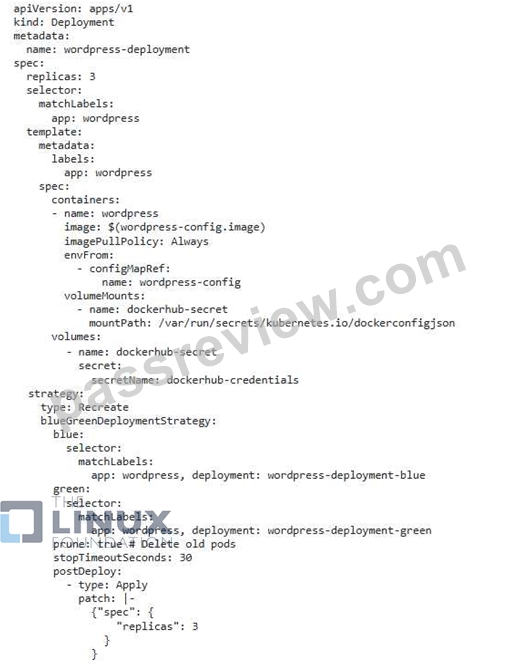
- Create a Kubernetes Service that exposes your WordPress application. This service will automatically route traffic to the active replica set.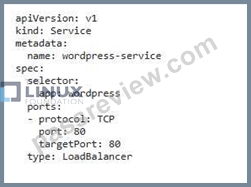
5. Automate the Blue-Green Deployment - Use a 'DeploymentConfig' resource to configure the automatic deployment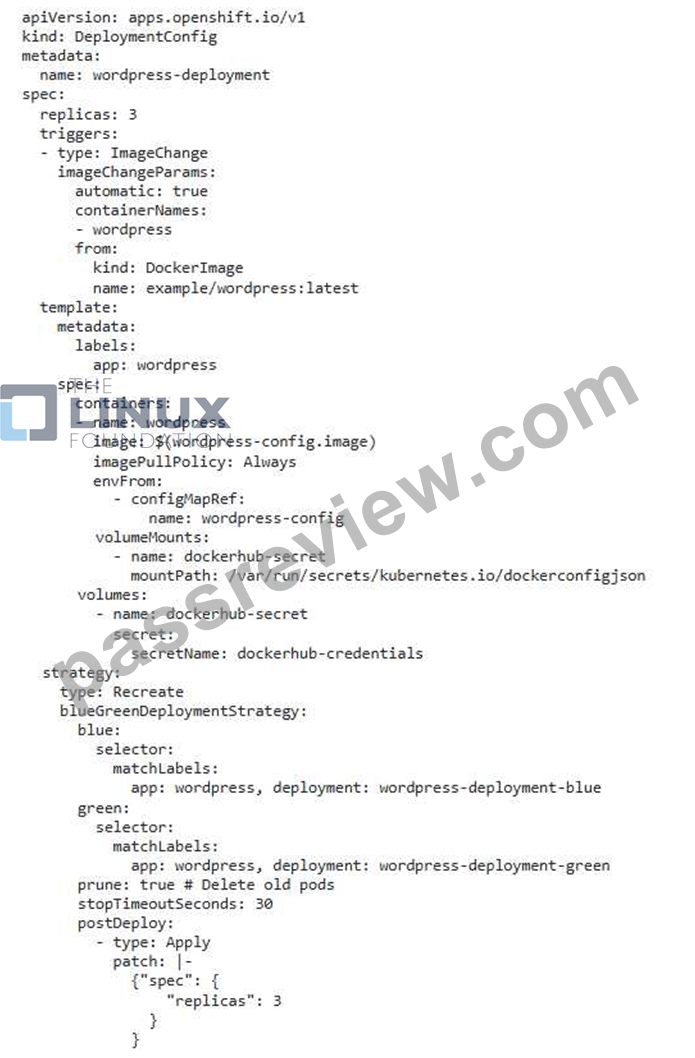
6. Apply the resources: - Apply all the YAML files using 'kubectl apply -f' to create the necessary resources. 7. Trigger the Blue-Green Deployment - Push a new image to the Docker Hub repository 'example/wordpress:latest' The 'Deploymentconfig' will automatically trigger the blue-green deployment: -A new replica set with the updated image will be created, and traffic will be shifted to the new replica set gradually - Once the traffic has been shifted, the old replica set will be deleted. Note: This implementation assumes that you are using OpenShift. If you are using a different Kubernetes distribution, the configuration may need to be adjusted SligntlY. ,
NEW QUESTION # 84
You have a Deployment for a web application that uses a separate Redis cache pod for session management. You want to ensure that each web application pod can access a dedicated Redis instance for session management and avoid contention. Explain how you can use a PersistentVolumeClaim and StatetulSet to achieve this.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
I). Create a PersistentVoIumeClaim:
- Create a PersistentVoIumeCIaim (PVC) to request persistent storage for each Redis instance.
- Specify the storage size, access modes, and other requirements based on your needs.
- Example: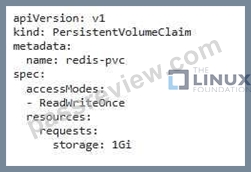
2. Create a StatefulSet: - Define a StatefulSet for the Redis pods. - Associate each Redis pod with a unique PVC, ensuring that each pod gets its own dedicated persistent volume. - Example: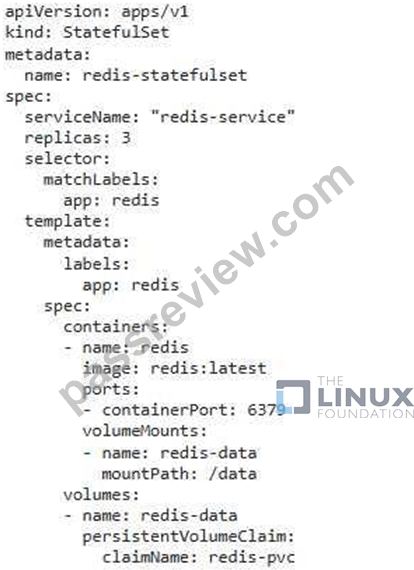
3. Configure the Deployment: - Denne tne web application pod Within a Deployment. - Use a Service (e.g., 'redis-service') to access the Redis instances. - Make sure the web application's code can access the Redis instances using the service name. - Example: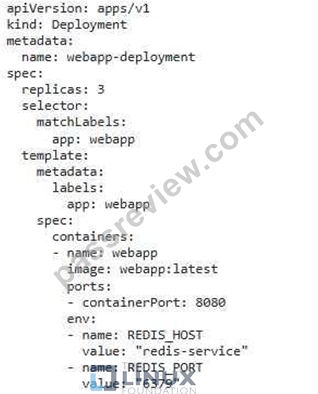
4. Deploy and Test - Deploy tne PersistentVolumeClaim, StatefulSet, and Deployment. - Test the web application to ensure that each pod can access its own dedicated Redis instance and session data is correctly managed Without contention. 5. Important: - StatefulSets ensure that each pod has a unique hostname and persistent storage, making them suitable for managing stateful applications. - This approach helps isolate Redis instances, preventing session data conflicts and ensuring the scalability of your web application. ,
NEW QUESTION # 85
You have a Deployment named 'wordpress-deployment' that runs 3 replicas of a Wordpress container. You need to set up resource requests and limits for CPU and memory for each pod. The application requires a minimum of 250m CPU and 512Mi memory, but it should not exceed 500m CPU and IGi memory. Furthermore, implement a resource quota for the swordpress' namespace to ensure that the total CPU requests and limits do not exceed 2 CPIJ and 4Gi memory, respectively.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Update the Deployment YAML:
- Add 'resources' to the 'containers' section, setting 'requests' and 'limits' for both CPIJ and memory.
- The 'requests' should be set to the minimum required resources, and 'limits' to the maximum allowed.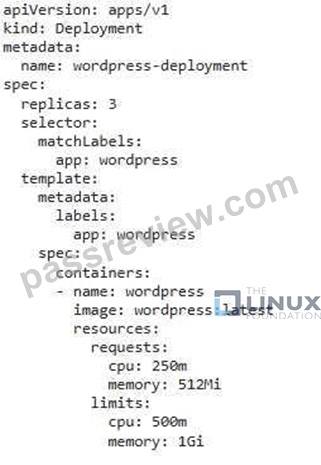
2. Create the Deployment: - Apply the updated YAML file using 'kubectl apply -f wordpress-deployment-yamr 3. Create a Resource Quota: - Create a ResourceQuota YAML file named 'wordpress-quota.yaml' with the following contents: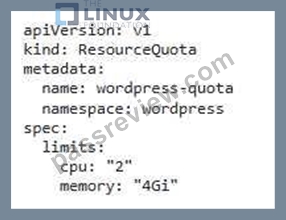
4. Apply the Resource Quota: - Apply the ResourceQuota YAML file using 'kubectl apply -f wordpress-quota.yamr. 5. Verify the Deployment and Quota: - Check the status of the Deployment using 'kubectl get deployments wordpress-deployment' to confirm the updated resource requests and limits. - Use ' kubectl get resourcequotas -n wordpresS to verify the applied resource quota and its remaining limits- 6. Test Resource Limits: - Try to create a new Deployment or Pod in the 'wordpress' namespace that exceeds the resource quota limits. This should result in an error, ensuring the quota is enforced.
NEW QUESTION # 86
You are building a new web application that utilizes a microservice architecture- One of the microservices, 'recommendation-service', is responsible for providing personalized product recommendations to users.
This service uses a machine learning model for generating recommendations based on user purchase history and browsing behavior. The model is trained offline and its weights are stored in a 'model-store' service.
Design a mufti-container Pod for the 'recommendation-service' that incorporates the following considerations:
- The Pod should include a primary container for the 'recommendation-service' application.
- The Pod should include a secondary container that runs the 'model-store' service to provide access to the trained model weights.
- Both containers should share a common volume to ensure that the model weights are available to the 'recommendation-service' container-
- The recommendation-service' snould be able to access the model weignts from the 'model-store' container witnout relying on a network call to another service-
- The recommendation-service' container should be configured to periodically update the model weights from the 'model-store' container when a new version of the model is available.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create the Deployment YAML:
- Define a Deployment with the name 'recommendation-service'
- Set the replicas to for redundancy and scalability.
- Specify the labels Sapp: recommendation-service' for selecting the Pods in the Deployment.
- Create a 'template' section to define the Pod specificatiom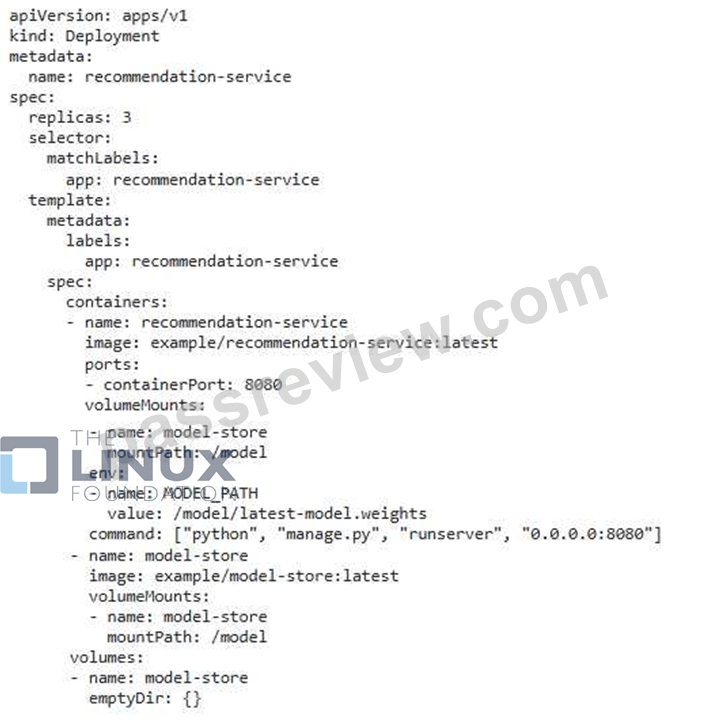
2. Deploy the Resources: - Apply the Deployment using 'kubectl apply -f deployment-yamp 3. Verify the Deployment: - Check the status of the Deployment using 'kubectl get deployments recommendation-service and ensure that three Pods are running. 4. Contigure the 'recommendation-service' - Modify the 'recommendation-service application to load the model weights from the specified path ClmodeVIatest-modeI_weightS). - Implement a mechanism within the 'recommendation-service to periodically check tor updated model weights in the shared volume. 5. Configure the 'model-store service: - Ensure that the model-store service is properly configured to store and retrieve the model weights. - Implement a mechanism in the 'model-store' service to notify the 'recommendation-service when a new model version is available. This notification can be achieved using a shared volume or a separate messaging system. 6. Test the Application: - Send requests to the 'recommendation-service' to generate recommendations. - Monitor the 'model-store' service and the shared volume to verify that the model weights are being updated correctly and the recommendation- service' is using the latest model version. Important Considerations: - Ensure that the 'recommendation-service' application is properly configured to access and load the model weights from the shared volume. - Implement a robust model management strategy, including versioning and rollback mechanisms, to ensure that the recommendation-service always uses the appropriate model. - Consider using a dedicated model store service that provides a dedicated API for retrieving and updating model weights. This can simplify the communication between the 'recommendation-service' and the model store. - Monitor the performance and resource usage of both services to ensure optimal performance.,
NEW QUESTION # 87
You have a Deployment running a web application that is scaling dynamically based on traffic. However, the application occasionally experiences Slow response times during peak traffic periods. You suspect that the pods are being scheduled on nodes that are already under pressure. To improve the performance, you want to implement node affinity, ensuring that pods are scheduled on nodes with specific labels that indicate high resources and low utilization.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Define Node Labels:
- Identify nodes with high resources and low utilization.
- Label these nodes with a specific label like 'high-resource':
bash
kubectl label nodes node-name high-resource=true
2. Configure Node Affinity in Deployment
- Update tne Deployment YAML to include node affinity rules.
- preferredDuringSchedulinglgnoredDuringExecution: This affinity rule indicates a preference for scheduling pods on nodes with specific labels. It doesn't prevent scheduling on other nodes if preferred nodes are unavailable.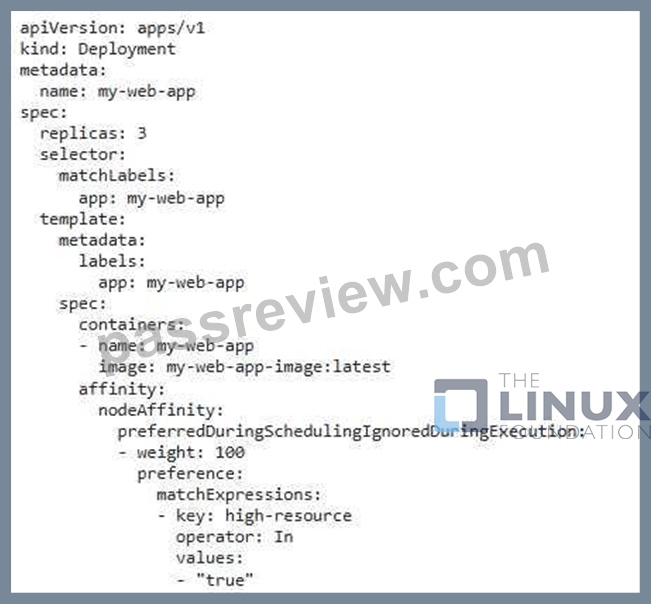
3. Apply the Deployment Configuration: - Apply the updated Deployment configuration to your Kubernetes cluster: bash kubectl apply -f my-web-app-deployment.yaml 4. Monitor Pod Scheduling: - Use 'kubectl get pods -l app=my-web-app' to monitor the pod scheduling. - Verity that the pods are being scheduled on nodes with the 'high-resource' label.
NEW QUESTION # 88
You must connect to the correct host . Failure to do so may result in a zero score.
[candidate@base] $ ssh ckad00034c
Task
A Deployment named content-marlin-deployment , running in namespace content-marlin is exposed via Ingress content-marlin-ingress .
The manifest files for the Deployment, Service and Ingress can be found at /home/candidate/content-marlin/.
The Deployment is supposed to be reachable at
http://content-marlin.local/content-marlin , but requesting this URL is currently returning an error.
Answer:
Explanation:
See the Explanation below for complete solution.
Explanation:
ssh ckad00034c
You're debugging an Ingress # Service # Deployment chain. The fastest way is:
* reproduce the error with the right Host header
* check Ingress rules (host/path/backend)
* check Service (selector/port/targetPort)
* check Endpoints (do we have ready pods?)
* fix the manifest(s) under /home/candidate/content-marlin/
* apply + re-test
Below are the exact commands + the most common fixes for this exact symptom.
1) Reproduce the failing request correctly
Even if DNS isn't set up, you can test with a Host header:
curl -i -H "Host: content-marlin.local"
http://127.0.0.1/content-marlin
If your ingress controller is not on localhost, find the NodePort/LoadBalancer IP. In these labs it's often localhost via a local proxy, but if needed:
kubectl get svc -A | egrep -i 'ingress|nginx'
kubectl get nodes -o wide
(But start with the localhost curl above.)
2) Inspect the provided manifests (this is what you must edit)
cd /home/candidate/content-marlin/
ls -l
sed -n '1,200p' *.yaml
Also view what's currently live in the cluster:
kubectl -n content-marlin get deploy,svc,ingress
kubectl -n content-marlin describe ingress content-marlin-ingress
kubectl -n content-marlin get ingress content-marlin-ingress -o yaml
What to look for in the Ingress:
* spec.rules.host should be content-marlin.local
* spec.rules.http.paths[].path should match /content-marlin
* Backend service name must be your service
* Backend service port must match the service port (name or number)
* pathType should be Prefix (usually safest)
3) Validate Service # Pod wiring (most common real cause)
3.1 Check service selector and ports
kubectl -n content-marlin get svc -o wide
kubectl -n content-marlin describe svc content-marlin-deployment 2>/dev/null || true kubectl -n content-marlin describe svc Identify the service that the Ingress points to (from describe ingress).
Check if the Service selector matches pod labels:
kubectl -n content-marlin get pods --show-labels
kubectl -n content-marlin get svc <SERVICE_NAME> -o jsonpath='{.spec.selector}{"\n"}'
3.2 Check endpoints (this tells you instantly if traffic can reach pods) kubectl -n content-marlin get endpoints kubectl -n content-marlin get endpoints <SERVICE_NAME> -o wide
* If ENDPOINTS is empty # Service selector doesn't match Pods OR Pods aren't Ready.
3.3 If endpoints empty, check pod readiness and labels
kubectl -n content-marlin get pods -o wide
kubectl -n content-marlin describe pod <pod-name>
4) Apply the most likely fix patterns
Fix pattern A: Ingress path needs rewrite
If your app serves / but you route /content-marlin, you often need rewrite.
Edit content-marlin-ingress manifest (in /home/candidate/content-marlin/) to include:
* path: /content-marlin
* pathType: Prefix
* annotation: rewrite to / (common for nginx ingress)
Example (typical nginx-ingress):
metadata:
annotations:
nginx.ingress.kubernetes.io/rewrite-target: /
spec:
rules:
- host: content-marlin.local
http:
paths:
- path: /content-marlin
pathType: Prefix
backend:
service:
name: <SERVICE_NAME>
port:
number: 80
If your ingress controller is not nginx, rewrite annotation may differ. But in CKAD labs, it's very often nginx.
Fix pattern B: Ingress points to wrong Service port
If the Ingress backend says port 80 but your Service exposes 8080 (or uses a named port), align them:
* Either change Ingress backend port.number
* Or change Service spec.ports[].port / targetPort
Fix pattern C: Service selector mismatch (endpoints empty)
If pods have label app=content-marlin but service selector is app=content-marlin-deployment (or vice versa), fix the Service selector to match pod labels.
Service should have:
spec:
selector:
app: <label-that-actually-exists-on-pods>
Fix pattern D: Service targetPort wrong
If container listens on 8080 but service targetPort is 80, fix it:
spec:
ports:
- port: 80
targetPort: 8080
5) Apply the corrected manifests
After editing the YAMLs under /home/candidate/content-marlin/:
kubectl apply -f /home/candidate/content-marlin/
Wait for readiness:
kubectl -n content-marlin rollout status deploy content-marlin-deployment kubectl -n content-marlin get endpoints kubectl -n content-marlin describe ingress content-marlin-ingress
6) Re-test the URL
curl -i -H "Host: content-marlin.local"
http://127.0.0.1/content-marlin
If you still get errors, also check ingress controller logs/events quickly:
kubectl -n content-marlin get events --sort-by=.lastTimestamp | tail -n 30 kubectl get pods -A | egrep -i 'ingress|nginx' The fastest way for you to finish in 1 shot Run these and paste the output (I'll tell you exactly which line to change and what to change it to):
kubectl -n content-marlin describe ingress content-marlin-ingress
kubectl -n content-marlin get svc -o wide
kubectl -n content-marlin get endpoints -o wide
kubectl -n content-marlin get pods --show-labels
sed -n '1,200p' /home/candidate/content-marlin/*.yaml
But even without pasting, if you follow steps 2-4 above, you'll find the broken link (Ingress rule, Service port, selector, or rewrite) and fix it cleanly.
NEW QUESTION # 89
You have a Kubernetes cluster with a namespace called 'dev' and a deployment named 'app-deployment' in that namespace. You need to create a new Role that allows users in the 'developers' group to only scale the Sapp-deployment' deployment. They should not be able to access any other resources in the 'dev' namespace. Implement the RBAC configuration for this scenario.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Role:
- Create a YAML file named 'scale-app-role.yaml' with the following content: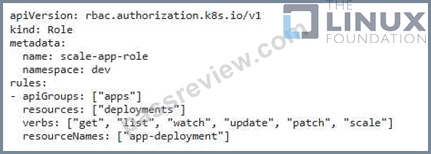
2. Create a RoleBinding: - Create a YAML file named 'scale-app-rolebinding.yaml' with the following content: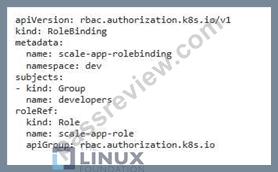
3. Apply the configuration: - Apply the Role and Role8inding using the following commands: bash kubectl apply -f scale-app-role.yaml kubectl apply -f scale-app-rolebinding-yaml 4. Verify the configuration: - You can verify the configuration by using the following command: bash kubectl auth can-i --list --as=user:testuser--group-developers--namespace-dev - Replace 'testuser' with the name of a user in the 'developers' group. The output should show only the following permissions: - 'apps/deployments': 'get, "list, 'watch', 'update', 'patch', 'scale' 5. Test the permissions: - Try to scale the Sapp-deployment deployment using the 'kubectr command as a user in the 'developers group. - Try to perform other actions on the deployment or other resources in the 'devs namespace. You should only be able to scale the Sapp-deployment deployment.
NEW QUESTION # 90
You are building a Kubernetes application tnat requires persistent storage for its dat a. The application needs to be able to access the data even if the pod is restarted or deleted. You have a PersistentVolumeClaim (PVC) defined for this purpose.
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a PersistentVolume (PV):
- Define a PV with a suitable storage class, access modes (ReadWriteOnce), and a capacity that meets your application's storage requirements.
- Example: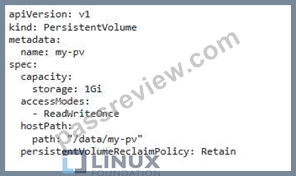
2. Create a PersistentVolumeClaim (PVC): - Define a PVC with the desired storage class and access modes. - Specify the desired storage capacity. - Example: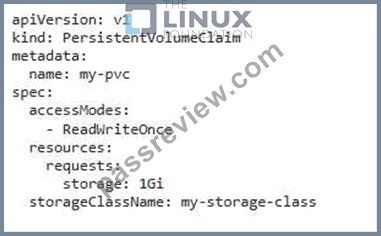
3. Create a Deployment With the PVC: - In the Deployment YAML, define a volume mount that uses the PVC you created_ - Specify the volume mount path within the container. - Example: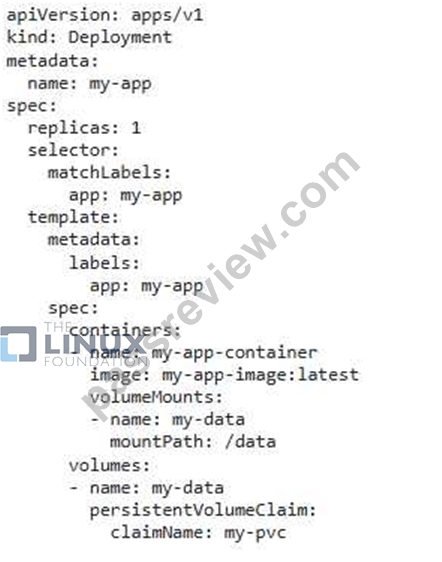
4. Create the Deployment: - Apply the Deployment YAML using 'kubectl apply -f my-app-deployment.yamr 5. Verify the Deployment - Check the status of the Deployment using 'kubectl get deployments my-app' - Verify that the Pod is running and using the PersistentVolumeClaim. - You can also check the pod's logs for confirmation that the data is stored in the mounted volume.
NEW QUESTION # 91
You are running a microservices application on Kubernetes, and you need to restrict the communication between your services to specific ports. For example, your 'frontend' service should only be allowed to communicate with the 'backend' service on port 8080. How would you configure this using NetworkPolicy in Kubernetes?
Answer:
Explanation:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Define the NetworkPolicy:
- Create a new YAML file (e.g., 'frontend-network-policy.yaml') to define the network policy.
- Specify the name of the NetworkPolicy and the namespace where it will be applied.
- Include the following elements within the 'spec' section:
- 'podSelector' to target the 'frontend' pods.
- 'ingress' section to define inbound traffic rules.
- 'egress' section to define outbound traffic rules.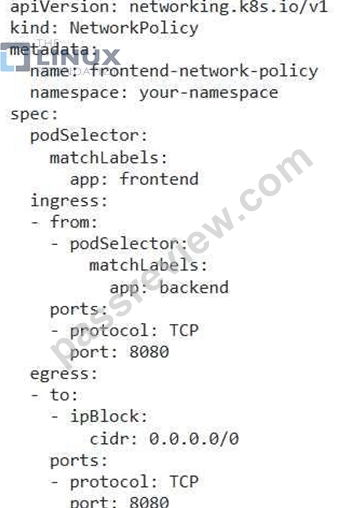
2. Apply the NetworkPolicy: - Apply the NetworkPolicy to your cluster using the following command: bash kubectl apply -f frontend-network-policy.yaml 3. Verify the NetworkPolicy: - Use the 'kubectl get networkpolicy' command to list the applied NetworkPolicies and confirm the status. 4. Test the Restrictions: - From a 'frontend' pod, attempt to connect to the 'backend' service on port 8080. - Attempt to connect to other services or ports on the backend or external networks. - Verify that the communication restrictions defined in the NetworkPolicy are working as expected.
NEW QUESTION # 92
......
CKAD Exam Dumps For Certification Exam Preparation: https://getfreedumps.passreview.com/CKAD-exam-questions.html